
"AI bot attacks" sounds new. In the access logs of the Joomla sites we maintain, it mostly looks like the old attacks done faster and at scale: thousands of requests probing known paths, login forms tried with leaked passwords, registration forms filled with spam, and crawlers copying every page. The automation is better. The defences that work are still the boring, specific ones.
This is how we harden a Joomla 5 or 6 site against automated traffic, starting with the changes that remove the most risk per minute of work.
Start with your own logs
Before you change anything, look at what is actually hitting the site. One command on the access log shows the most requested paths that don't exist:
# terminal – top 404s in the last log (nginx/Apache combined format)
awk '$9 == 404 {print $7}' /var/log/nginx/example.com.access.log | sort | uniq -c | sort -rn | head -25
On a typical Joomla site the list includes:
/api/index.php/v1/config/application?public=true. This probes CVE-2023-23752, the Joomla 4.0.0–4.2.7 flaw that exposed the configuration, database password included, without login. It is still one of the most scanned Joomla URLs. On a patched site it returns 403 or 404, and the request is only noise./configuration.php.bak,/configuration.php~,/.git/config,/.env. Leftovers from editors, deploys and backups./administrator/with POST requests: password guessing./component/users/?view=registration: registration spam.
Each of these maps to one of the fixes below.
1. Keep code and secrets out of the web root: the public folder
Since Joomla 5.0, a site can serve only a public folder, which holds the entry points and the public media. configuration.php, libraries/, administrator/components/ and everything else stay one level up, where no URL can reach them. A leftover configuration.php.bak is then simply not downloadable.
# terminal – run once, then point the virtual host's document root at the new folder
php cli/joomla.php site:create-public-folder --public-folder=/var/www/example.com/public --live-site=https://example.com
Test it on staging first. Extensions that write files to their own folder and link to them by URL can break, because only the folders the public folder exposes are reachable. On new sites we use it from day one.
2. Put a second lock on /administrator
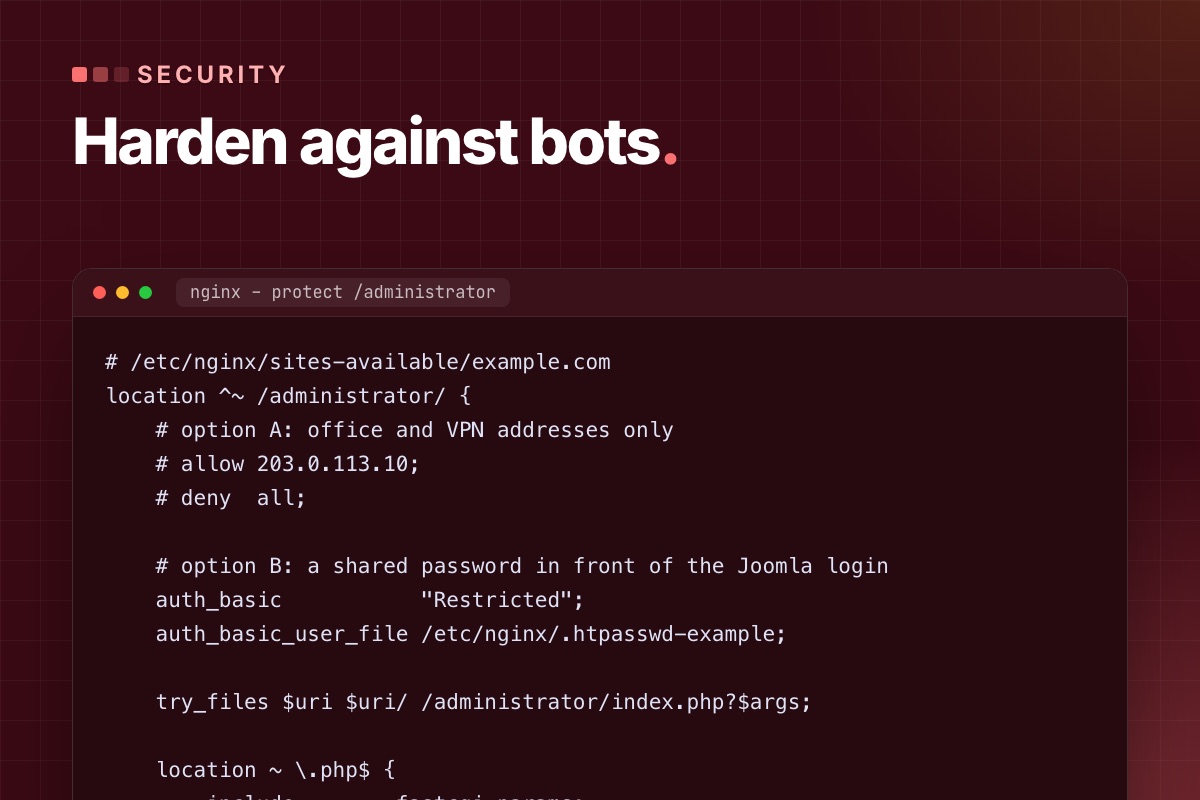
Joomla's own login is not the problem. Exposing it to the whole internet is. If the editors work from known places, allow only those addresses. If they don't, add HTTP authentication in front, so bots never reach Joomla's login form at all:
# /etc/nginx/sites-available/example.com
location ^~ /administrator/ {
    # option A: office and VPN addresses only
    # allow 203.0.113.10;
    # deny  all;

    # option B: a shared password in front of the Joomla login
    auth_basic           "Restricted";
    auth_basic_user_file /etc/nginx/.htpasswd-example;

    try_files $uri $uri/ /administrator/index.php?$args;

    location ~ \.php$ {
        include        fastcgi_params;
        fastcgi_param  SCRIPT_FILENAME $document_root$fastcgi_script_name;
        fastcgi_pass   unix:/run/php/php8.3-fpm.sock;
    }
}
Keep the PHP handler inside this block. A location ~ \.php$ elsewhere in the config matches /administrator/index.php first and skips the password, which is the most common mistake we find in "protected" admin folders.
3. Turn off what you don't use: Web Services and registration
- The API. If nothing talks to
/api/, disable the "API Authentication" plugins (Basic and Token) and the Web Services plugins, or deny/api/in the web server. If you do use it, use Token authentication for one dedicated user with the minimum permissions, never a Super User account. - User registration. If the site has no members area, set Users → Options → "Allow User Registration" to No. If it has one, add the proof-of-work CAPTCHA (Joomla 6.1+) to the registration form and require admin or email activation.
4. Make stolen passwords useless: enforce MFA
Joomla 4.2 and later include multi-factor authentication with passkeys (WebAuthn), TOTP apps, YubiKey, email codes and backup codes. The setting most sites miss is enforcement: Users → Options → Multi-factor Authentication → Enforce Multi-factor Authentication for the Super Users and Administrator groups. Without it, MFA is optional and the accounts that matter most often don't have it.
While you're there, audit who actually has Super User rights:
# terminal – every Super User, with the last visit (adjust the prefix)
mysql -e "SELECT u.id, u.username, u.email, u.block, u.lastvisitDate
          FROM jos_users u JOIN jos_user_usergroup_map m ON m.user_id = u.id
          WHERE m.group_id = 8 ORDER BY u.lastvisitDate DESC;" mydb
Accounts of former developers and agencies show up on almost every site we take over. Block them, don't just change their passwords.
5. Slow down password guessing
Bots rotate IP addresses, but most still send many POSTs from each one. A rate limit on login requests costs real users nothing:
# /etc/nginx/conf.d/limits.conf
limit_req_zone $binary_remote_addr zone=joomla_login:10m rate=10r/m;

# /etc/nginx/sites-available/example.com – inside location ^~ /administrator/
location = /administrator/index.php {
    limit_req zone=joomla_login burst=5 nodelay;
    limit_req_status 429;
    # … fastcgi lines as above
}
The same zone works for the front-end login (/component/users/ or your login menu item). Joomla's "Maximum MFA tries" and "MFA limit block time" options cover the second factor.
6. Make uploads harmless
Most real Joomla compromises we clean up started with a file upload: an old extension that accepted a PHP file disguised as an image. Two layers:
- Media options: keep "Restrict Uploads" and "Check MIME Types" on, and keep the allowed extensions to what editors need. The Joomla 6 defaults are sensible: images incl.
webpandavif, office files, PDF, audio, video. - The web server: never execute PHP in folders that hold uploads. Even if a PHP file gets in, it is served as text or blocked:
# /etc/nginx/sites-available/example.com – before the general PHP location
location ~* ^/(images|media|tmp|cache|logs)/.*\.(php|phtml|phar)$ {
    deny all;
}
7. Send security headers from Joomla
The core System – HTTP Headers plugin sets HSTS, X-Frame-Options, Referrer-Policy, Cross-Origin-Opener-Policy and a Content-Security-Policy, and it supports nonces and script hashes for the CSP. Turn the CSP on in report-only mode first and read the reports for a week. Third-party widgets and inline scripts in old modules will show up there. Enforcing a CSP blindly breaks pages.
8. Know when a file changes
An attacker who gets in drops a backdoor and leaves. You find out months later. The cheapest file-integrity check is version control on the server: commit a clean state and look at the difference.
# terminal – once, on a clean site (keep .git outside the public folder or deny it in the web server)
cd /var/www/example.com
git init -q && git add -A && git commit -qm "baseline $(date +%F)"

# daily, from cron: anything changed that wasn't an update you made?
git status --porcelain | grep -vE '^( M|\?\?) (cache|tmp|administrator/logs|images)/'
Without Git, compare against a clean package of the same Joomla version with diff -rq. A modified core file is either a hack someone made years ago or a backdoor, and you want to know which.
9. Patch on time, not "soon"
Automated attacks start within days of a public advisory. Subscribe to the Joomla Security Centre feed, and from Joomla 6.2 on, look at the security flag on extension updates: the dashboard highlights updates that their vendor marked as security releases, with a severity. A routine of "check updates every Monday, security updates the same day" beats any firewall rule.
10. AI crawlers: decide, then enforce
Crawlers that collect training data (GPTBot, ClaudeBot, CCBot, Google-Extended and others) are not attacks. Whether you allow them is a business decision: blocking them keeps your content out of training sets, and may also keep your site out of AI answers. The well-known ones respect robots.txt:
# robots.txt – opt out of AI training crawlers, keep search engines
User-agent: GPTBot
User-agent: ClaudeBot
User-agent: CCBot
User-agent: Google-Extended
Disallow: /
Scrapers that ignore robots.txt need rate limits or a bot-management rule at the CDN. They're a load problem more than a security one, and the page cache helps more than blocking.
If you are already compromised
- Take a full copy (files and database) before cleaning, as evidence and so you can compare later.
- Put the site offline (
php cli/joomla.php site:down) and change the database, FTP/SSH and hosting passwords. - Compare the files against a clean Joomla package and clean copies of each extension. Look in
images/andtmp/for PHP files. - Check
#__usersfor new Super Users and#__extensionsfor plugins you didn't install. - Find the way in (usually an outdated extension in the access log around the first changed file), patch it, then go back online.